Introduction to Kryptic
Updated
Kryptic is a developer secrets platform that injects environment variables at runtime - no .env files in your repo, no secrets in CI config.
A local daemon authenticates once via your browser, then your apps pull secrets over a local socket at startup. Add a kryptic.json to your repo root and one SDK line - that is the entire integration. Works on macOS, Linux, and Windows.
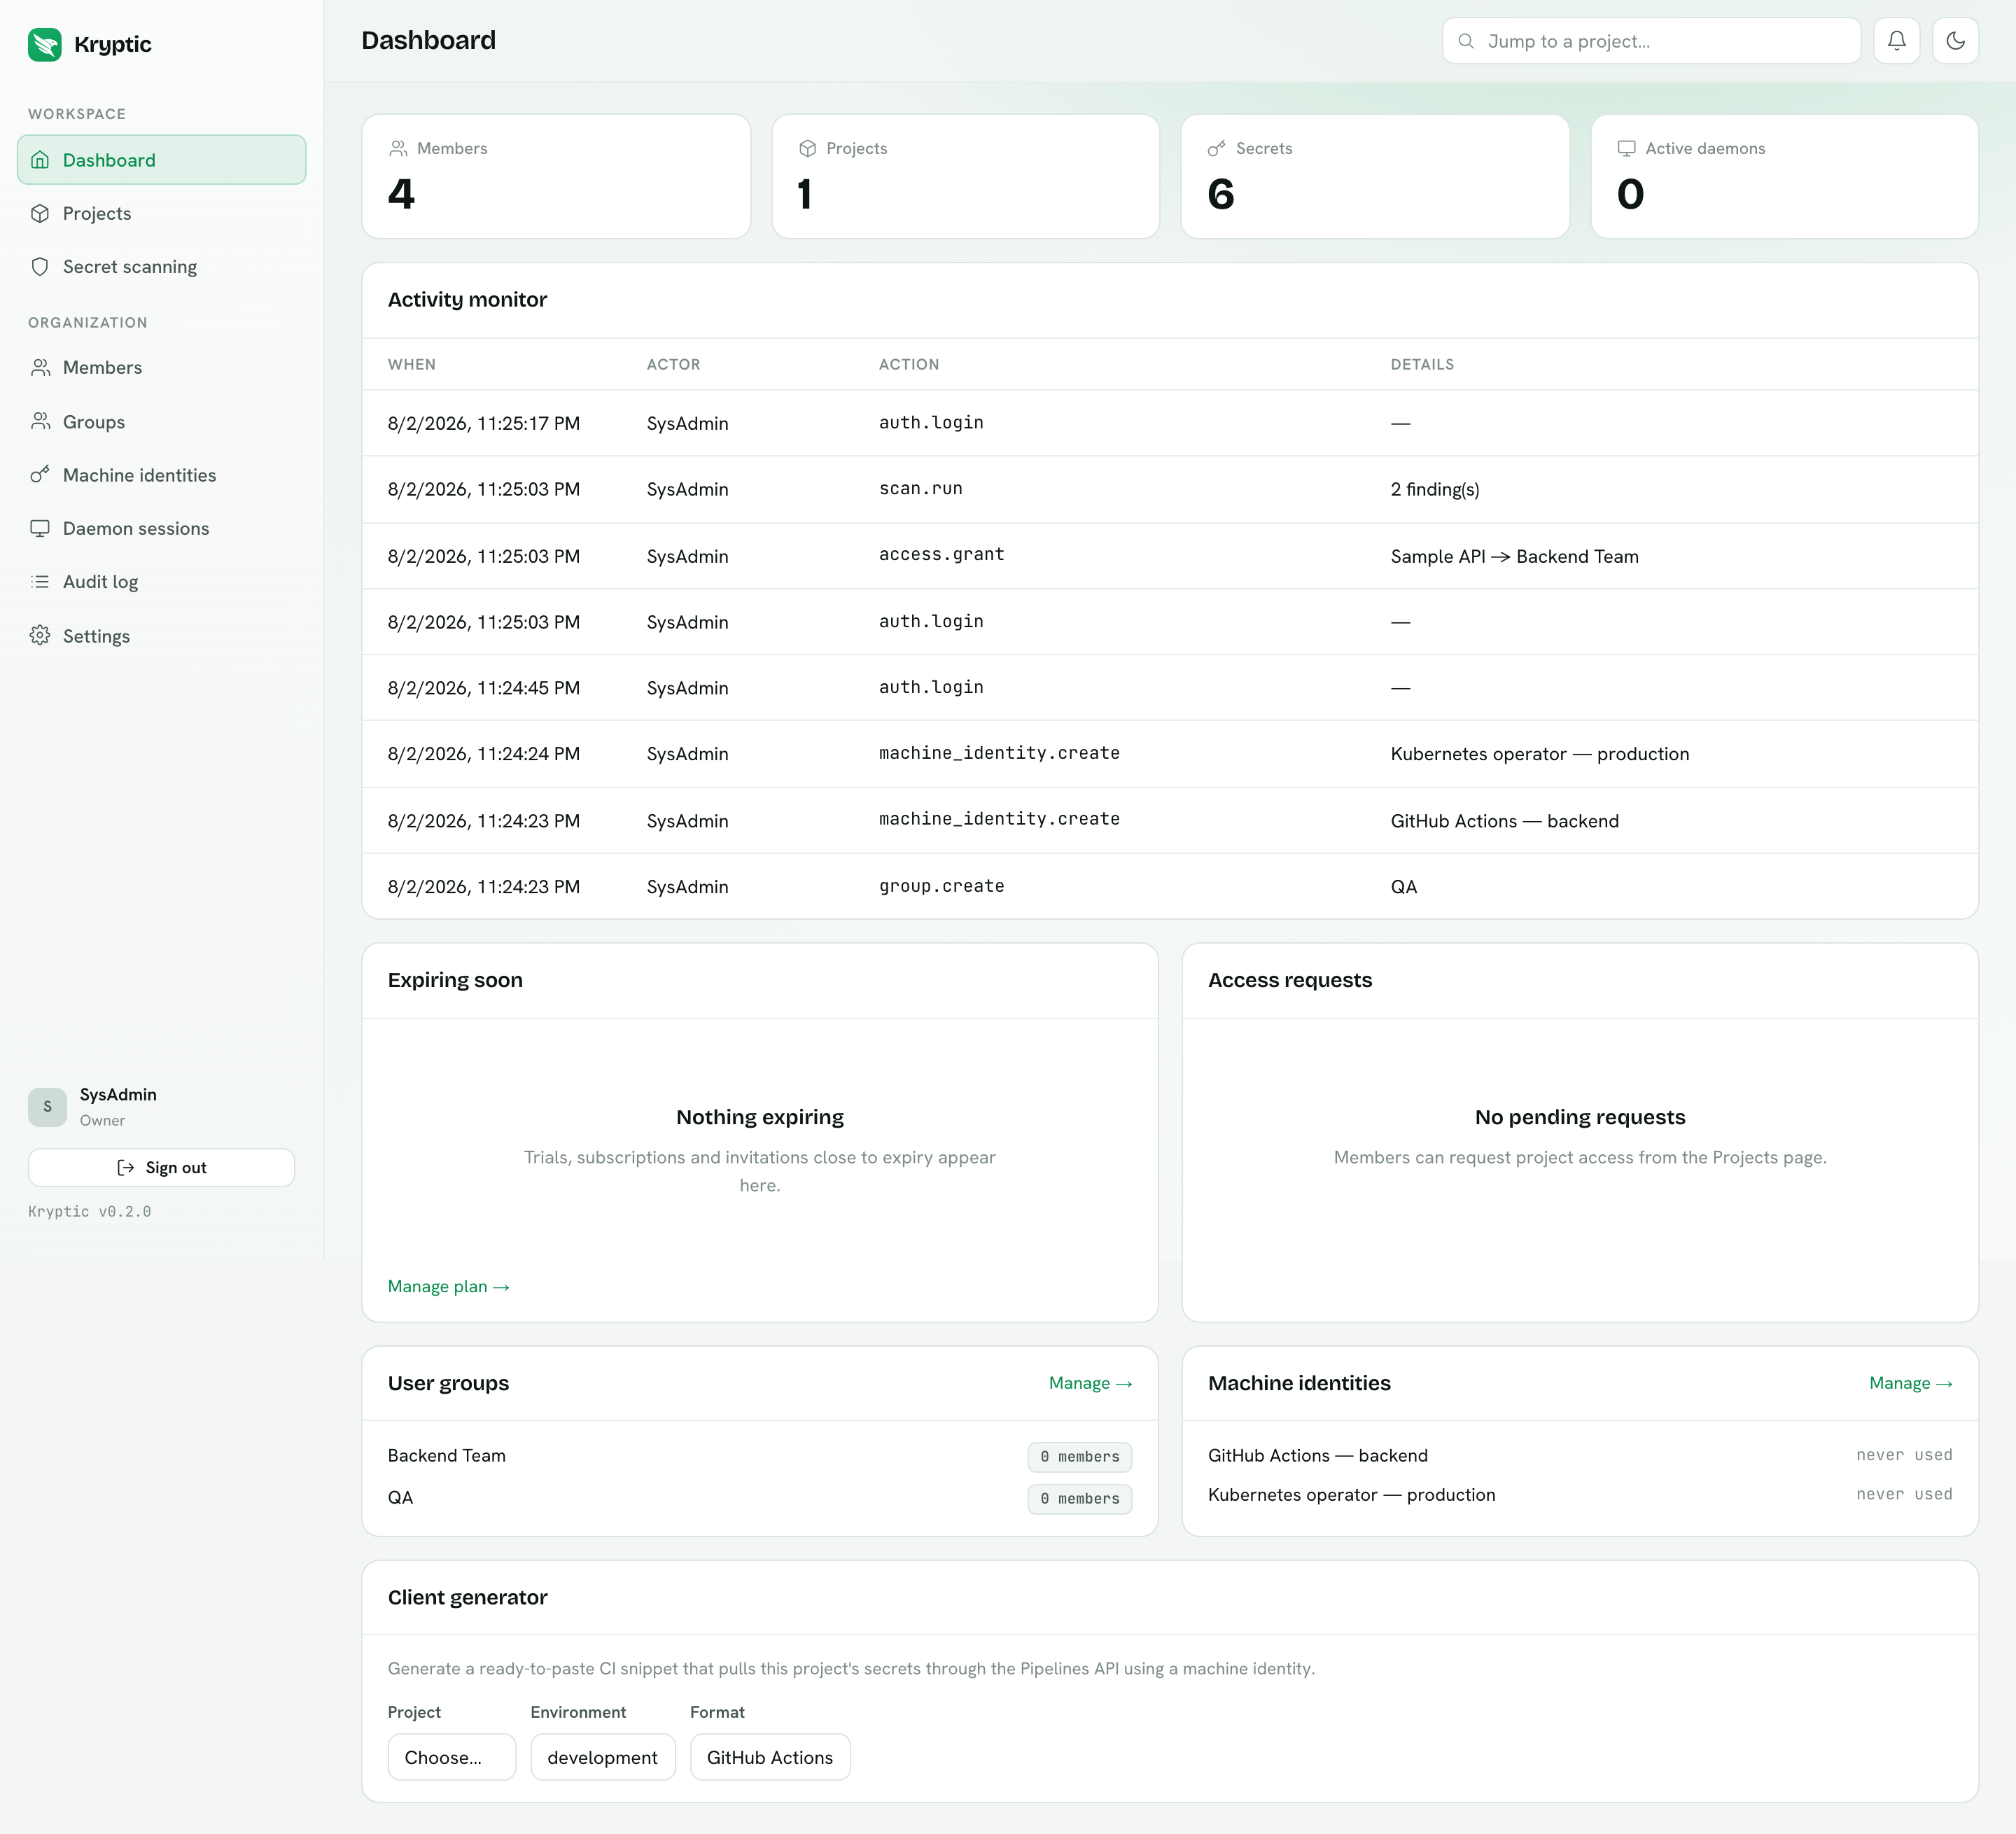
Your team manages projects, environments, access and audit history from the dashboard; developers never leave their editor.
Open-source clients
Anything that can see a secret in plaintext is open source and lives under github.com/dev-kryptic. The server platform is proprietary: it stores ciphertext it has no path to open. See Encryption.
| What | GitHub | Published as | License |
|---|---|---|---|
| Daemon and CLI | Kryptic.Daemon | kryptic binary | GPL-3.0 |
| Encryption engine (.NET) | Kryptic.Encryption.Net | NuGet Kryptic.Encryption | Apache-2.0 |
| Encryption engine (TypeScript) | Kryptic.Encryption.NPM | npm @krypticdev/encryption | Apache-2.0 |
| Encryption engine (Go) | Kryptic.Encryption.Go | Go module github.com/dev-kryptic/Kryptic.Encryption.Go | Apache-2.0 |
| Kubernetes operator | Kryptic.K8s.Operator | GitHub Release + ghcr.io/dev-kryptic/kryptic-operator | Apache-2.0 |
| Language SDKs | Kryptic.Net, Node, Python, Java, Go, Ruby, Cpp, Rust | Kryptic.Daemon.Client / @krypticdev/daemon-client / kryptic-daemon-client | Apache-2.0 |
Each Kryptic SDK is intentionally thin: one entry point that talks to the local daemon. It contains no authentication or secret-storage logic.
Documentation
Quickstart
Install the daemon, sign in once, run your app - about three minutes.
Language SDKs
Lightweight, language-native SDKs for .NET, Node.js, Python, Java, Go, Ruby, C++, and Rust.
CLI reference
Every kryptic command: lifecycle, auth, secrets, CI export, scanning, self-update.
Configuration
The kryptic.json schema and the environment variables every SDK honors.
The dashboard
A tour of every screen: projects, secrets, members, audit and billing.
Org shared secrets
One organization catalog, project org references, and the Business plan gate.
Access control
Roles, per-environment grants, groups and access requests.
Encryption
Blind store, organization key, and the three public encryption-engine repos.
For geeks
Wire formats, key hierarchy, and the exact hop where ciphertext becomes plaintext.
Self-hosting
Run the full platform yourself with Docker Compose or Helm.
Coolify
Inject secrets at container start with a machine identity and kryptic ci export.
REST API v1
Programmatic access to projects and secrets with machine identities.
Enterprise SSO
SAML 2.0 single sign-on and SCIM 2.0 user provisioning.
Dynamic secrets
Leased credentials through a customer-side connector. Enterprise only.